Digitally sign applications, exchange trusted business documents and secure internal infrastructure with a professionally managed Private PKI.
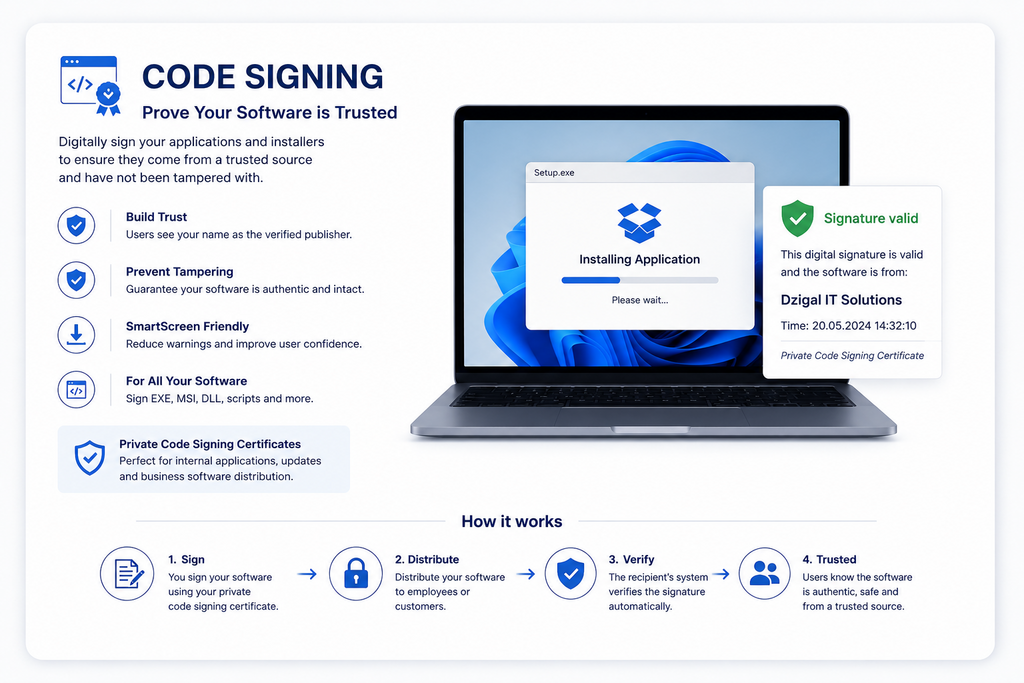
Whether you develop internal business applications or distribute software to trusted customers, our managed Code Signing service helps you prove software authenticity, protect against tampering, and establish digital trust—without investing in your own PKI infrastructure.
Ideal for:
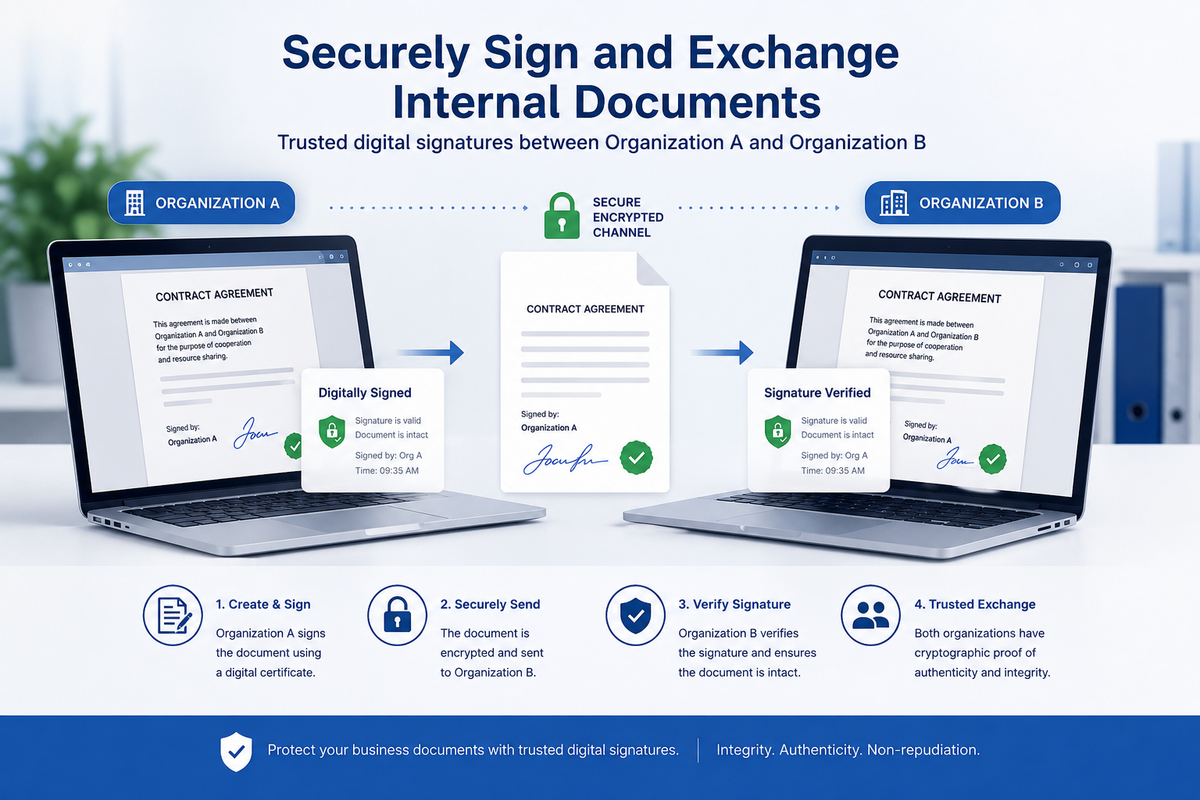
Need to exchange contracts, reports or business documents with another trusted organization?
Our managed Private PKI enables both organizations to verify document authenticity, integrity and origin using digital certificates.
Certificates issued through the Dzigal Private PKI are intended for private trust environments and are not publicly trusted by default.
The Dzigal Root CA must be explicitly installed and trusted on participating devices or systems. When certificates are used between two organizations, both parties must establish trust in the Dzigal Private PKI before relying on the issued certificates.
For services that must be trusted automatically by anyone on the Internet.
✓ Public websites
✓ Public SSL/TLS
✓ Automatic browser and OS trust
✓ Internet-facing services
For organizations that need secure certificates inside their own trusted environment.
✓ Internal applications and servers
✓ Document signing
✓ Internal code signing
✓ Internal SSL/TLS
✓ Employee and device certificates
✓ Certificate revocation and lifecycle management
Dzigal operates a private PKI and is not a publicly trusted global Root Certificate Authority.
Certificates issued by Dzigal are trusted only on devices and systems where the Dzigal Root CA has been installed and explicitly trusted.
This makes the service suitable for companies, internal networks, business applications and controlled organizational environments.
